

Defense in Depth: The Wordfence Approach to WordPress Security
TL;DR: Don’t rely on a single security layer. For a comprehensive defense in depth approach to WordPress security trusted by over 5 million sites, install Wordfence.
Wordfence’s 5 million site network produces the most comprehensive WordPress threat intelligence available — attacks we see across millions of sites inform our firewall rules and malware signatures, delivered in real-time to Premium users and after 30 days to free users.
Most WordPress security plugins work like a single deadbolt to your front door. They stop basic break-in attempts but ultimately leave you vulnerable to sophisticated attackers with better tools.
Your business is worth more than that. Just like you have cameras, locks, and passwords protecting your physical space, you likewise need a comprehensive security infrastructure for your WordPress website.
Wordfence fulfills this exact requirement of modern WordPress websites with its defense in depth framework built specifically for WordPress, thanks to its multiple barriers working together. Let’s take a look at what Wordfence’s defense in depth looks like and what it offers for WordPress security.
Table of Contents
What Is Defense in Depth?
Defense in depth is a cybersecurity strategy built on one core idea: no single layer of protection is enough. Instead of relying on one tool or control, a defense in depth approach stacks multiple layers of security, each designed to detect, prevent, or mitigate threats at different stages of an attack.
In practice, this means combining proactive and reactive measures:
- Firewalls block malicious traffic before it reaches your site.
- Malware scanners identify and remove infections from compromised or suspicious files.
- Login security, file integrity monitoring, and real-time threat intelligence further strengthen the perimeter and protect internal systems.
For a helpful primer on defense in depth and how Wordfence incorporates this principle, watch Part 2 of our WordPress Security Essentials Course:
Watch the full WordPress Security Essentials Course in less than 20 minutes.
Why Defense in Depth Is a Must-Have for WordPress Security
Modern WordPress attackers are sophisticated. They don’t just try one method; they use multiple vectors simultaneously. This becomes a problem if your security solution only blocks brute force attacks; it might be useless against plugin vulnerabilities that offer pathways for SQL injections.
Adopting single-layer security solutions also creates false confidence. They make website owners believe they’re protected, so they continue to build up their website with third-party plugins. The problem? Up to 96% of WordPress vulnerabilities come from plugins. So the more plugins you have installed, the more potential attack vectors that exist for malicious actors to exploit — something single-layer security solutions can’t defend against.
Plus, with artificial intelligence in the mix, attacks are getting increasingly complex, much faster than single-layer defenses can adapt.
That’s why, for WordPress, defense in depth ensures that even if one layer is bypassed, others continue to safeguard your site. It’s a resilient, sweeping approach — one that transforms security from a single point of failure into a comprehensive, adaptive system.
The Wordfence Defense in Depth Framework
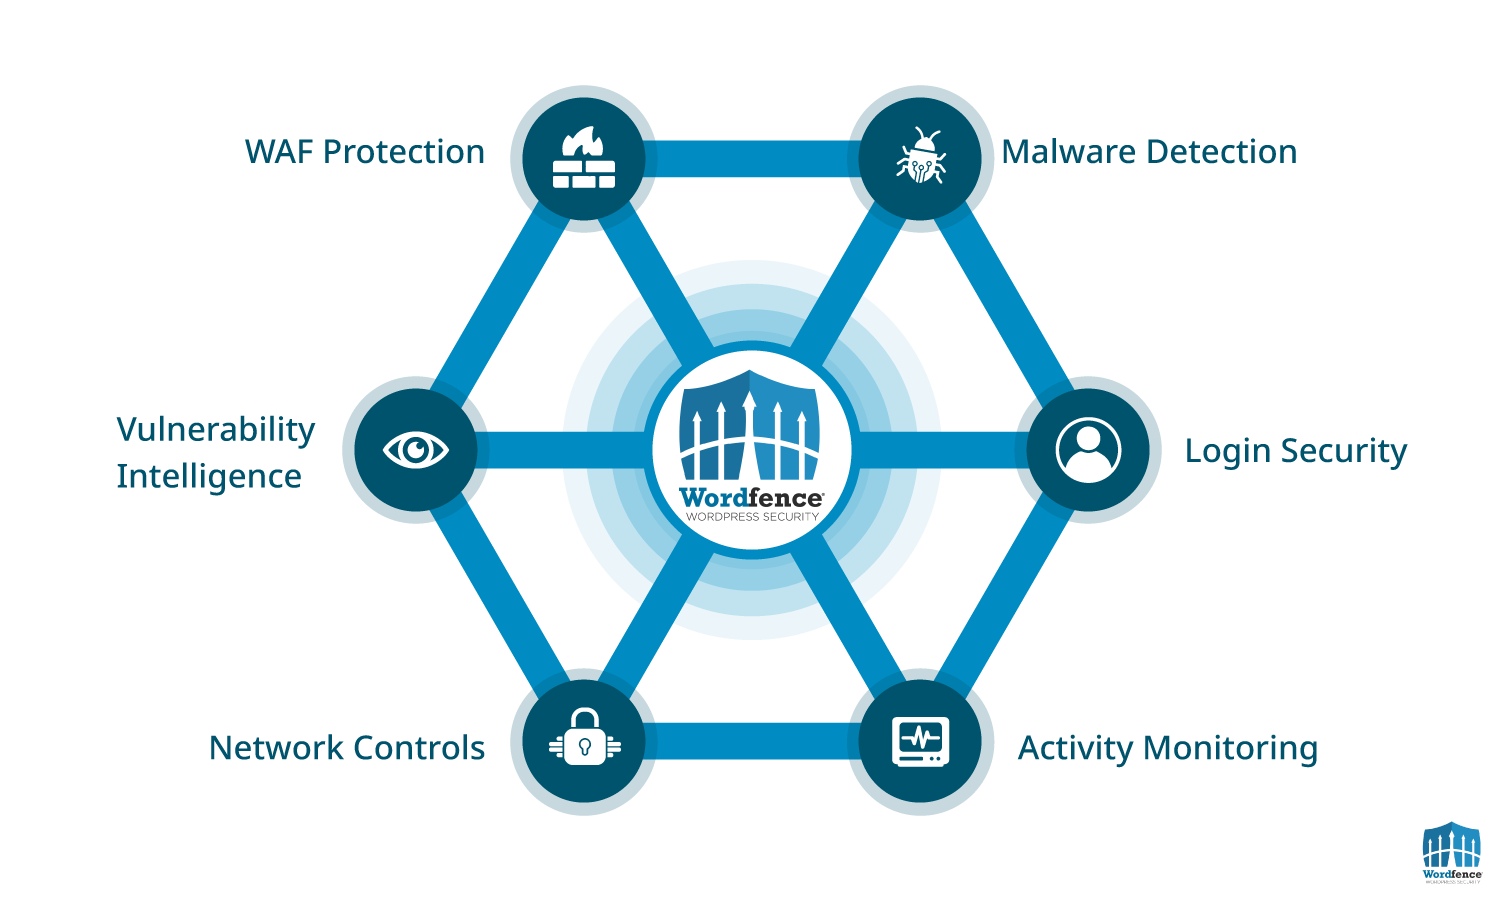
Wordfence’s robust defense in depth framework is based on more than 10 years of WordPress-specific security research and the remediation of tens of thousands of WordPress websites.
Acting as a frontline defender of over 5 million WordPress websites, we know the threats your WordPress website faces, and in all of our plans, including Wordfence Free and Wordfence Premium, we’ve engineered a comprehensive system of security layers to stop all those threats in their tracks.
Let’s explore how they work together to provide a layered defense for WordPress websites.
In This Section
Web Application Firewall Protection
Wordfence runs an endpoint firewall directly on your WordPress server. Unlike cloud firewall solutions, it isn’t vulnerable to the “Cloud Firewall Bypass Problem.” Notably, it’s a WordPress-specific threat intelligence solution that understands WordPress internals in a way that’s not possible with generic web firewalls.
The Wordfence web application firewall (WAF) provides a solid front-line defense against malicious actors by blocking SQL injection, XSS, and remote file inclusion attacks before they reach the WordPress core.
Wordfence blocked over 54 billion malicious requests in 2024, and we deployed 117 WordPress-specific firewall rules to Wordfence plugin users. We provide real-time firewall rule updates based on the latest threat intelligence for paid users, and Wordfence Free users also get these updates after a 30-day delay.
To learn more about our endpoint firewall and why it’s miles better at protecting your website than the cloud-based firewalls offered by competitors, check out our blog post on why Wordfence offers the best WordPress firewall.
Advanced Malware Detection and Removal
Server-side malware scanning accesses files that remote scanners cannot. This provides protection against backdoors, spam injectors, SEO spam, cryptocurrency miners, and other similar threats. It can even detect deeply-embedded malware due to its server-level access.
Wordfence includes one-click malware removal, even in the free version. Wordfence alternatives either charge extra for this feature or omit malware removal entirely. Just note that it’s important to follow website security best practices, like maintaining regular backups and understanding the nature of the files you modify, to prevent unintentional changes that could break your website.
Wordfence also offers a file integrity monitoring feature that detects unexpected changes to WordPress core files. Our Threat Intelligence Team also regularly adds new malware signatures to it to protect against evolving malware threats, like this formjacking vulnerability.
On top of that, higher-tier Wordfence products — Wordfence Care and Wordfence Response — come with incident response services for businesses looking for reliable external support and timely remediation.
Vulnerability Protection Through Threat Intelligence
Wordfence’s team of security experts operates the largest WordPress vulnerability research program in the industry.
The Wordfence Bug Bounty Program incentivizes researchers to report vulnerabilities to Wordfence first. At publication, we’ve awarded $638,850 in bounties for published vulnerabilities — with rewards of up to $32,760. So far, this program has uncovered more than 5,500 threats, contributing to the more than 29,900 unique vulnerabilities in plugins and themes recorded in our Threat Intelligence database, which actively helps protect websites against even forgotten or abandoned plugins.
Another important aspect of our approach includes a responsible disclosure process. We coordinate with developers to fix the issue at the root while simultaneously creating protective rules. As a result, we offer zero-day protection for users before most attackers are even aware of vulnerabilities that could be exploited. Thus, our threat intelligence feeds directly into firewall rules.
Beyond protecting individual sites, we help secure the entire WordPress community by publishing our research for free. As the largest CVE Numbering Authority (CNA) in the WordPress ecosystem, we publish CVEs (common vulnerabilities and exposures) that contribute to the larger threat intelligence community, ensuring that security information is accessible to all defenders.
Comprehensive Login Security
Wordfence offers rate limiting that distinguishes legitimate users from malicious bots. We blocked over 55 billion password attacks in 2024 alone, which can be attributed to our comprehensive approach to login security.
Importantly, this includes strong password enforcement for users and admins, as well as country blocking for login pages (with Wordfence Premium). However, these measures are not always enough. When it comes to web applications, such as WordPress, 88% of breaches involved stolen credentials.
That’s why Wordfence also offers password leak detection that monitors data breaches for your site’s user credentials and built-in 2FA you can force for all users (or only certain user roles, such as admins). Other security plugins either lack all of these features or only offer a fraction, forcing you to depend on additional plugins that increase your attack surface area.
Network-Level Controls
Unlike competitors, Wordfence includes hundreds of default rules against common attack patterns and historical plugin vulnerabilities out of the box. And for those looking for more granular levels of control, Wordfence supports blocking specific IP addresses or a set of IP addresses via custom patterns.
With Wordfence, you also have the option to blanket ban certain high-risk countries from accessing your whole website (or even just the login form) via country blocking — a premium-only feature.
Additionally, as the leading WordPress security plugin, Wordfence gets the most robust attack data to pinpoint malicious IPs known for attacking WordPress websites and prevents them from accessing your website via our real-time IP blocklist (another premium-only feature).
Professional Incident Response
With a physical break-in, you can always call the police to seek a resolution. The ideal response isn’t quite the same when it comes to cyberspace: businesses must identify and vet suitable cleanup solutions. This search can be a daunting task when you’re dealing with the prospect of extra downtime, data theft, and permanent reputational damage.
No matter the severity of the incident, Wordfence is your best ally if your site has been compromised. Besides our comprehensive security scanner and one-click malware removal tool, we also offer incident response services with higher-tier plans.
Wordfence Care comes with unlimited incident response and hands-on support during business hours. And for mission-critical websites seeking minimal downtime, Wordfence Response offers a 24/7/365 1-hour incident response guarantee for a speedy fix.
By contrast, other security solutions either don’t offer a cleanup service, charge per fix, or take days to clean up a website that you need to be operational in hours — not ideal.
Complete Website Activity Monitoring
Wordfence offers real-time visibility into all website activity and security events. Our detailed Audit Log (for Premium, Care, and Response plans) tracks all administrative actions and suspicious activity, which offers insights into potential threats affecting your WordPress website.
Wordfence also lets you customize notifications so you can understand what’s happening on your site in real time, empowering you to take action if necessary. You can choose the types of alerts you want to receive via email. Additionally, with our free centralized website management system, Wordfence Central, you can choose additional channels, including email, Slack, Discord, and SMS.
Defense in Depth: How the Layers Work Together

Wordfence offers a truly comprehensive defense in depth solution by weaving all these layers together:
- Shared intelligence: Our firewall solution is enhanced by an extensive database of malware signatures and known vulnerabilities, shielding your website against malware and attacks designed to exploit hidden backdoors.
- Redundant protection: The Wordfence firewall filters out unwanted traffic, rate limits protect against bot attacks, and leaked password protection guards against unsafe passwords. Then, there’s two-factor authentication (2FA) that requires using additional login verification methods like an authenticator app. If a threat manages to work its way through all of this, there’s activity monitoring and malware scanners (plus removal) as well to help identify and eradicate issues.
- Synergy: Without vulnerability protection against specific WordPress threats, a web application firewall (WAF) is severely limited. Similarly, you need a firewall to reinforce your login protection. These layers work in tandem to keep your website safe.
Implement Wordfence’s Defense in Depth Approach Today
Don’t wait. Implement Wordfence’s layered, defense in depth website security solution today. By using one plugin that does it all, you also benefit from another WordPress security best practice — reducing the attack vectors associated with installing multiple plugins.
Get started by installing, configuring, and scanning your website with Wordfence Free.
From there, you can choose the plan that best fits your needs: Wordfence Premium, Wordfence Care, or Wordfence Response.